SOC Analyst Course Eligibility: Who Can Learn SOC in 2026?
If you are interested in cybersecurity but are not sure whether you are eligible to learn SOC, the good news is that SOC training is not limited to experienced cybersecurity professionals.
Students, freshers, IT professionals, networking learners, system administrators, and career-switchers can build SOC skills by starting with the right fundamentals.
In 2026, entry-level SOC roles commonly expect knowledge of networking, SIEM, log analysis, Windows/Linux, security fundamentals, incident response, and security monitoring. Current Hyderabad job postings also show demand for SIEM and endpoint-security skills, including QRadar and SentinelOne. (areteir.wd1.myworkdayjobs.com)
The important question is therefore not only “Am I eligible?”, but:
“Do I have the interest and willingness to learn the technical skills required for SOC work?”
⭐ 5 Highlights Students Should Know
1. 🎓 Freshers Can Start SOC Training
You don’t necessarily need previous SOC experience to begin learning. Freshers can start with networking, operating systems, cybersecurity fundamentals, and then progress to SIEM and security monitoring.
2. 💻 Basic IT Knowledge Is Helpful
You don’t have to be an expert programmer. However, understanding computers, networks, Windows/Linux, and basic troubleshooting will make the learning process easier.
3. 🔐 Practical Skills Matter
Modern SOC roles emphasize practical skills such as SIEM, log analysis, alert triage, incident response, EDR/XDR, and threat investigation. (Cyber Defence)
4. 🚀 Non-Cybersecurity Students Can Build Their Foundation
Students from IT-related backgrounds can transition into SOC by learning the fundamentals systematically. Non-IT students may need additional time for computer, networking, and operating-system basics.
5. 🧠 Analytical Thinking Is as Important as Technical Knowledge
A SOC Analyst needs to investigate evidence, identify patterns, distinguish genuine threats from false positives, document findings, and communicate conclusions clearly.
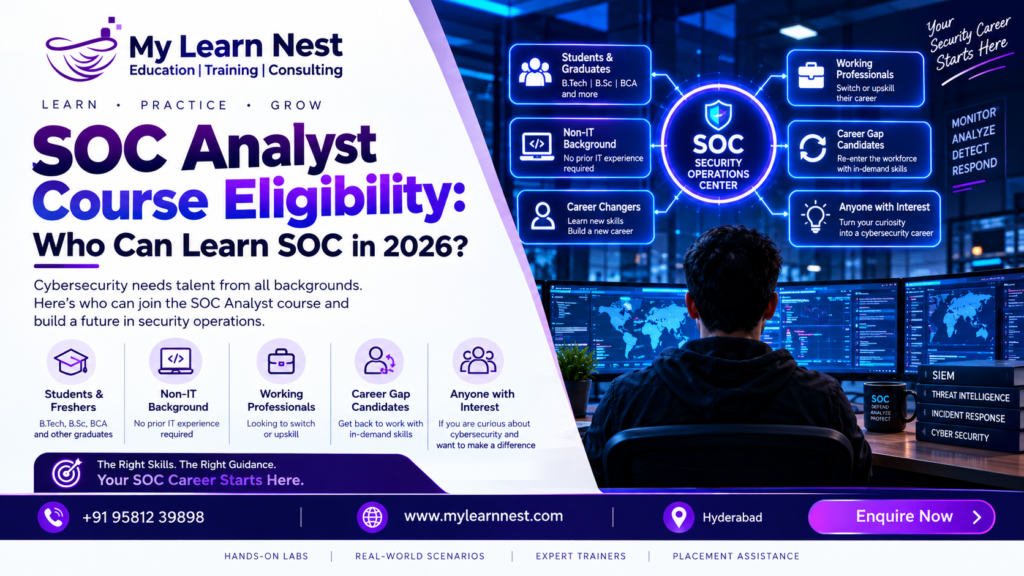
Who Is Eligible for a SOC Analyst Course in 2026?
There is no single academic background that automatically makes someone a SOC Analyst.
The following learners can consider SOC training.
🎓 B.Tech / B.E. Students & Graduates
Students from:
- Computer Science
- Information Technology
- Cybersecurity
- Electronics
- Computer Engineering
- Related technical branches
may find the transition relatively straightforward because they may already have exposure to computers, programming, operating systems, or networking.
💻 BCA / MCA Students
BCA and MCA students can also consider SOC as a cybersecurity career path.
Their programming and computer fundamentals can be useful when learning:
- Networking
- Windows/Linux
- SIEM
- Security monitoring
- Log analysis
- Python
- PowerShell
🌱 Freshers
If you are a fresher with limited professional experience, you can start by building your fundamentals.
A beginner-friendly path is:
Computer Fundamentals
↓
Networking
↓
Windows & Linux
↓
Cybersecurity
↓
SIEM
↓
Log Analysis
↓
Incident Response
↓
SOC Projects
↓
Interview Preparation
Can Non-IT Students Learn SOC?
Yes, but expect a longer learning curve.
Students from non-IT backgrounds should first become comfortable with:
- Basic computer concepts
- Operating systems
- Networking
- IP addresses
- Ports
- DNS
- Web basics
- Security fundamentals
You do not need to become an expert in all these topics before starting.
Instead, learn them alongside your SOC training.
A simple approach:
Computer Basics → Networking Basics → Cybersecurity → SOC Tools → Practical Investigation
This gives beginners a much stronger foundation.
Do You Need Programming to Become a SOC Analyst?
No, you don’t need to be a professional software developer.
However, basic scripting can become valuable as you progress.
For example:
PowerShell
Useful for understanding and investigating Windows activity.
Python
Useful for:
- Log processing
- Automation
- Data analysis
- Simple security scripts
Current cybersecurity guidance also increasingly highlights basic scripting and automation as useful SOC skills. (EICTA Consortium)
So don’t worry if you aren’t a programmer.
Start with basic scripting, not advanced software development.
Do You Need a Cybersecurity Degree?
A cybersecurity degree can be helpful, but students should not assume that a degree alone makes them job-ready.
Employers may look for a combination of:
- Education
- Technical knowledge
- Practical skills
- SIEM exposure
- Security understanding
- Communication
- Problem-solving
- Projects
- Relevant experience
Some current entry-level guidance lists bachelor’s degrees as common, but the requirements vary by employer. (nexsonitacademy.com)
Therefore, focus on skills + practical experience + a strong resume, not just the qualification.
🛡️ What Skills Should You Have Before Starting SOC Training?
You don’t need all of these on Day 1.
But having basic knowledge in these areas can make learning easier.
Computer Fundamentals
- Operating systems
- Files and folders
- Processes
- Users
- Applications
- Basic troubleshooting
Networking
- TCP/IP
- IP addresses
- DNS
- HTTP/HTTPS
- Ports
- Firewalls
- VPN
- Basic network traffic
Operating Systems
- Windows
- Linux
- Users and permissions
- Event logs
- Processes
- Authentication
Cybersecurity
- Malware
- Phishing
- Ransomware
- Brute-force attacks
- Vulnerabilities
- Authentication
- Security controls
🔥 What Do You Actually Learn in SOC Training?
A good SOC learning roadmap should gradually move from fundamentals to practical security operations.
Core Modules
Module 1: Cybersecurity Fundamentals
Module 2: Networking Fundamentals
Module 3: Windows Security
Module 4: Linux Security
Module 5: SIEM Fundamentals
Module 6: Microsoft Sentinel
Module 7: KQL
Module 8: Splunk & SPL
Module 9: IBM QRadar
Module 10: EDR/XDR
Module 11: Log Analysis
Module 12: Alert Triage
Module 13: Incident Response
Module 14: Threat Intelligence
Module 15: MITRE ATT&CK
Module 16: Threat Hunting
Module 17: PowerShell & Python Basics
Module 18: Practical SOC Projects
Module 19: Interview Preparation
🚀 SOC Analyst Eligibility Roadmap for Beginners
If you are starting from zero, follow this roadmap.
Stage 1 — Understand Computers
Learn:
- Computer fundamentals
- Operating systems
- Users
- Processes
- Files
- Basic troubleshooting
Goal: Understand what you’re protecting.
↓
Stage 2 — Learn Networking
Study:
- TCP/IP
- DNS
- HTTP/HTTPS
- Ports
- Firewalls
- VPN
- Network traffic
Goal: Understand how devices communicate.
↓
Stage 3 — Learn Windows & Linux
Understand:
- Windows Event Logs
- Authentication
- Processes
- Linux logs
- Users
- Permissions
- PowerShell basics
Goal: Understand what normal and suspicious system activity looks like.
↓
Stage 4 — Learn Cybersecurity
Study:
- Phishing
- Malware
- Ransomware
- Brute-force attacks
- Credential attacks
- Vulnerabilities
- Indicators of compromise
Goal: Understand common attack techniques.
↓
Stage 5 — Learn SIEM
Start with:
- Microsoft Sentinel
- KQL
- Splunk
- SPL
- IBM QRadar
Goal: Learn how SOC analysts monitor and investigate security events.
↓
Stage 6 — Practise Alert Investigation
Work through scenarios such as:
- Failed login
- Successful login after multiple failures
- Phishing
- Malware
- Suspicious PowerShell
- Unusual network activity
Goal: Develop an investigation mindset.
↓
Stage 7 — Learn Incident Response
Understand:
Detection → Analysis → Containment → Eradication → Recovery
Goal: Know what happens after identifying a real threat.
↓
Stage 8 — Build Practical Projects
Create investigations around:
- Phishing
- Brute force
- Malware
- Account compromise
- Endpoint attacks
- Threat hunting
Goal: Build practical evidence for your resume and interviews.
↓
Stage 9 — Prepare for Interviews
Practise:
- Technical questions
- SOC scenarios
- SIEM questions
- Log analysis
- Incident-response questions
- Mock interviews
Goal: Become confident explaining your investigation process.
📅 6-Month Roadmap for Students
Month | Focus |
Month 1 | Computer + Networking Fundamentals |
Month 2 | Windows + Linux + Cybersecurity |
Month 3 | SIEM + Log Analysis |
Month 4 | Sentinel + KQL + Splunk + QRadar |
Month 5 | EDR + Incident Response + Threat Hunting |
Month 6 | Projects + Resume + Mock Interviews + Job Preparation |
This roadmap can be adjusted according to your existing knowledge and the amount of time you can dedicate to practice.
🎯 How Do You Know If SOC Is Right for You?
Ask yourself these questions:
Do you enjoy solving problems?
SOC investigation requires you to look at evidence and determine what happened.
Are you interested in cybersecurity?
You will continuously encounter new attacks, tools, vulnerabilities, and techniques.
Do you like analysing information?
SOC analysts often examine logs, alerts, IP addresses, domains, processes, and user activity.
Are you willing to learn continuously?
Cybersecurity changes quickly. Current industry guidance emphasizes adaptability and continuous learning as important professional skills. (EICTA Consortium)
Are you comfortable with shift-based work?
Many SOC operations provide 24/7 monitoring, particularly at L1. Students should understand this before choosing the career path. (Cyber Defence)
If your answer is yes, SOC could be worth exploring.
🔎 What Are Employers Looking for in SOC Analysts in 2026?
Current job descriptions and 2026 industry guidance repeatedly point toward several core skills.
Technical Skills
- SIEM
- Log analysis
- Networking
- Windows/Linux
- Incident response
- EDR/XDR
- Threat intelligence
- MITRE ATT&CK
- Query languages such as KQL or SPL
- Basic scripting
For example, a current Hyderabad Security Analyst posting specifically mentions SIEM, QRadar, threat monitoring, threat hunting, indicators of compromise, and TTP analysis. (areteir.wd1.myworkdayjobs.com)
Another Hyderabad SOC posting mentions monitoring with Splunk, Microsoft Sentinel, or Elastic SIEM, along with investigation and escalation. (APPIT Software Solutions)
This means students should avoid choosing training based only on certificates. Practical exposure matters.
🌟 MyLearnNest Institute — SOC Analyst Training in Hyderabad
Start Your Cybersecurity Journey With the Right Foundation
For students searching for SOC Analyst Training in Hyderabad, MyLearnNest can provide a structured learning path designed to help beginners progress from fundamentals to practical SOC skills.
The focus should be:
Learn → Practise → Investigate → Build → Prepare → Apply
Instead of simply memorizing cybersecurity definitions, students should understand how security teams investigate actual alerts.
Training Areas Can Include:
✔ Networking fundamentals
✔ Windows security
✔ Linux security
✔ Cybersecurity fundamentals
✔ SIEM
✔ Microsoft Sentinel
✔ KQL
✔ Splunk
✔ IBM QRadar
✔ EDR/XDR
✔ Log analysis
✔ Alert triage
✔ Incident response
✔ Threat intelligence
✔ Threat hunting
✔ MITRE ATT&CK
✔ PowerShell
✔ Python basics
✔ SOAR fundamentals
✔ Practical SOC projects
✔ Interview preparation
💡 Why Students Can Consider MyLearnNest
1. Beginner-Friendly Learning
Students can start with the fundamentals before moving into advanced SOC concepts.
2. Practical Security Skills
The learning path can focus on investigating alerts and analysing security evidence rather than only memorizing theory.
3. Industry-Relevant Tools
Students can gain exposure to:
Microsoft Sentinel + KQL + Splunk + QRadar + EDR/XDR
These technologies align with tools appearing in current SOC and security job descriptions. (areteir.wd1.myworkdayjobs.com)
4. Practical Projects
Students can work through scenarios involving:
- Phishing
- Brute-force
- Malware
- Suspicious login
- Endpoint alerts
- PowerShell activity
- Threat hunting
5. Career & Interview Preparation
Students can prepare for:
- SOC L1 interviews
- Technical assessments
- Scenario-based questions
- Resume building
- Job applications
🎓 Is MyLearnNest Suitable for Freshers?
If you are a fresher, don’t think:
“I have no experience, so I can’t learn SOC.”
Instead, think:
“I need to build the skills that an entry-level SOC role requires.”
Start with fundamentals.
Then learn the tools.
Then practise investigations.
Then build projects.
Then prepare for interviews.
That’s a much more realistic path toward your first cybersecurity opportunity.
🚀 From Student to SOC Analyst
Your journey can look like this:
Student
↓
Networking Learner
↓
Cybersecurity Beginner
↓
SOC Trainee
↓
SIEM Practitioner
↓
SOC Project Builder
↓
Interview-Ready Candidate
↓
SOC Analyst L1
↓
SOC Analyst L2
↓
Threat Hunter / Incident Responder / Detection Engineer
Your first SOC role is not the final destination. It can become the foundation for several cybersecurity career paths.
Frequently Asked Questions
Can freshers learn SOC in 2026?
Yes. Freshers can start by building networking, operating-system, cybersecurity, SIEM, and log-analysis fundamentals.
Can a non-IT student learn SOC?
Yes, but non-IT students may need additional time to learn computer, networking, and operating-system fundamentals.
Do I need programming knowledge?
No advanced programming knowledge is required for an entry-level SOC learning path. Basic PowerShell or Python can become useful as you progress.
Is a cybersecurity degree mandatory?
Not necessarily. Requirements vary by employer. Education can help, but practical skills and relevant knowledge are also important.
Which SIEM should I learn first?
Start with SIEM fundamentals, then gain practical exposure to one or more platforms such as Microsoft Sentinel, Splunk, or IBM QRadar.
Is SOC suitable for freshers?
Yes, particularly L1 SOC roles, although employers may have different educational, technical, and experience requirements.
What is more important: certification or practical skills?
Both can help, but don’t rely on certification alone. Practical investigation skills, SIEM knowledge, projects, and the ability to explain your work are valuable.
Final Takeaway
Who can learn SOC in 2026?
The answer is broader than many students think.
You can consider SOC training if you are:
🎓 A college student
💻 A B.Tech/B.E. graduate
🖥️ A BCA/MCA graduate
🌱 A fresher
🔧 A networking learner
🖥️ An IT support professional
🔐 A cybersecurity beginner
🔄 Someone planning a career transition
You don’t need to know everything before you begin.
You need a structured learning path and the willingness to practise.
The ideal progression is:
Computer Basics → Networking → Windows/Linux → Cybersecurity → SIEM → Log Analysis → Incident Response → Threat Hunting → Projects → Interview Preparation
For students in Hyderabad, a practical SOC Analyst Course in Hyderabad should therefore focus on both fundamentals and hands-on security operations.
🚀 Your SOC journey can start with one decision:
Learn the fundamentals. Practise the tools. Investigate the alerts. Build your skills. Prepare for the opportunity.
MyLearnNest can be positioned as a structured learning option for students and freshers who want to develop practical SOC Analyst skills and prepare for entry-level cybersecurity careers.

